
AI Solutions
AI-Powered Business Execution Platform
Attackers exploit enthusiasm for AI agents, increasingly familiar QR codes, and commercialized malware tools to evade enterprise defenses
Check out Keypoint Intelligence’s Cybersecurity page!
HP has published the September 2026 edition of its Wolf Security Threat Insights Report, detailing cyberattack trends observed during Q2 2026. As with their previous quarterly research, HP’s findings highlight attackers’ continued reliance on social engineering, legitimate tools, and multi-stage infection chains to bypass enterprise security controls.
One of the most notable developments is how cybercriminals are capitalizing on enthusiasm surrounding agentic AI. Rather than using sophisticated AI to conduct attacks, threat actors are exploiting users’ growing willingness to trust AI-powered tools with increasingly sensitive tasks and information.
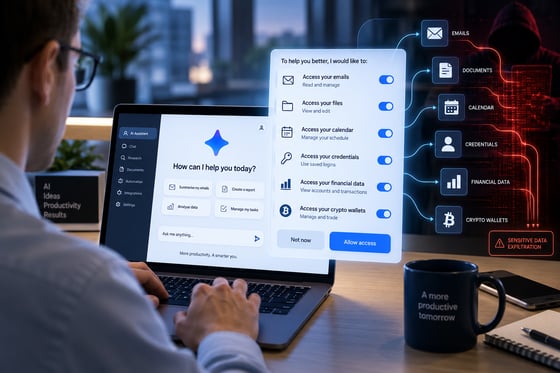
AI Agents and the Risks of Delegated Access
(Source: OpenAI ChatGPT)
Attackers are also taking advantage of another increasingly familiar technology—QR codes—to shift phishing attacks from protected PCs onto smartphones, while off-the-shelf malware continues to fuel a growing malware marketplace.
Three campaigns identified by HP illustrate how attackers are exploiting both emerging technologies and increasingly routine user behaviors.
AI Trading Agent Delivers Needle Stealer
AI agents capable of independently carrying out tasks are rapidly gaining attention, and cybercriminals appear keen to capitalize on that momentum.
For instance, HP Sure Click detected a campaign built around a website advertising what appeared to be an AI-powered cryptocurrency trading assistant. The site promoted a personalized trading bot that could follow a user-defined strategy and automatically trade cryptocurrency on the user’s behalf. Its name deliberately resembled that of a well-known AI assistant, while attackers used search engine poisoning and paid advertising to attract potential victims. Instead, users who downloaded the advertised software received an archive containing Needle Stealer malware.
The infection chain used a legitimate Microsoft-signed executable and DLL sideloading before running the malware inside a legitimate process. Needle Stealer then searched Chromium-based browsers for popular cryptocurrency wallet extensions, replacing them with convincing malicious copies designed to capture wallet credentials and provide access to victims’ funds.

Needle Stealer Malicious Browser Extensions
(Source: HP Wolf Security Threat Insights Report, September 2026)
The campaign matters beyond cryptocurrency theft. Users are becoming increasingly comfortable asking AI systems to perform work on their behalf and providing them with access to sensitive information, accounts, and financial data. This creates another opportunity for social engineering, as requests for extensive access may appear less suspicious when users believe it is necessary for an AI agent to perform a delegated task.
Quishing Moves the Attack from PC to Smartphone
HP also identified phishing campaigns using QR codes embedded in PDF invoices. Known as “quishing,” the technique takes advantage of both the familiarity of QR codes and a potential gap between desktop and mobile security controls.
The PDFs displayed a blurred invoice alongside a QR code and instructions for recipients to scan it with their smartphones to access the document. This led through several redirects before reaching a fake Microsoft login page designed to steal credentials. Importantly, scanning the code moves the attack from a corporate PC, where the malicious URL may already be blocked, to a smartphone where the same protections may not be present.
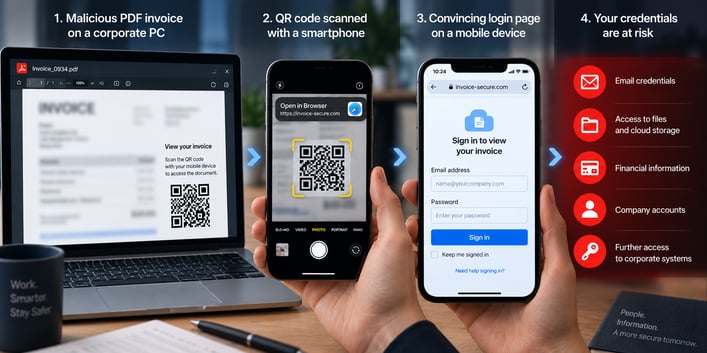
How Quishing Moves an Attack from PC to Smartphone
(Source: OpenAI ChatGPT)
For organizations, the significance is that QR codes are becoming a routine part of payments, authentication processes, product information, and documents. Users may therefore be less suspicious of scanning a QR code than clicking an unfamiliar hyperlink, despite both potentially leading to the same malicious destination.
The campaign demonstrates that organizations need to consider the entire user workflow when assessing phishing exposure. Protecting the PC does not necessarily protect the user if an attacker can persuade them to continue the same interaction on another device.
Phantom Stealer Brings a Commercial Model to Malware
Another campaign isolated by HP Sure Click highlights the increasingly commercial nature of cybercrime.
Phantom Stealer is an information-stealing tool marketed as a “penetration testing tool,” with performance claims, continuous updates, and even 24/7 buyer support. The offering includes both a stealer for extracting sensitive information and a crypter designed to protect the payload from analysis.
HP observed Phantom Stealer being distributed through malicious email attachments, using PowerShell, malware concealed inside an image, and process injection to execute the stealer. A related component called Phantom Gate acts as the loader, with HP suggesting the two may originate from the same source.
The significance is that attackers increasingly do not need to develop every component themselves. Ready-made malware, loaders, and delivery tools can be combined into functioning campaigns, lowering the technical expertise and effort required to launch attacks.
Threat Landscape by the Numbers
HP Sure Click telemetry showed that executables remained the most common malware delivery type during Q2 2026, accounting for 40% of threats, followed by archives at 38%. PDF threats declined from 10% to 8%, while Word-based threats fell from 7% to 6% and Excel threats increased from 4% to 6%.
Email remained the dominant threat vector at 56%, followed by web browser downloads at 24% and other vectors at 20%. Notably, 10% of email threats had already bypassed one or more email gateway scanners before being detected at the endpoint.
HP also observed increased use of Cloudflare Turnstile, a legitimate bot-detection service that attackers can use to hinder automated security analysis while allowing real users to continue to malicious content.
Keypoint Intelligence Opinion
The September 2026 HP Wolf Security Threat Insights Report reinforces a trend visible in the company’s earlier research: cybercriminals do not necessarily need fundamentally new attack techniques when they can become better at packaging, distributing, and disguising existing ones.
Agentic AI adds a new dimension. Earlier HP research identified signs of AI-assisted malware development, while the Needle Stealer campaign demonstrates how AI itself can become the social-engineering lure. This matters as users increasingly delegate tasks to AI applications and provide them with access to accounts, files, credentials, and financial information. Requests for broad access may start to appear normal, making it harder to distinguish approved AI tools from convincing imitations.
Quishing illustrates a related problem. Attackers are exploiting behaviors users increasingly regard as routine, while potentially moving an interaction from a protected corporate PC onto a less-protected smartphone.
Phantom Stealer, meanwhile, demonstrates how commercialized malware and supporting tools continue to lower the technical barrier for attackers.
The common thread across HP’s findings is trust. A Microsoft-signed executable looks trustworthy. A QR code on an invoice looks routine. A professionally presented software service looks legitimate. And an AI agent promising to perform a complex task autonomously can appear particularly attractive. As attackers become better at reproducing these signals of legitimacy, organizations will need security controls that provide protection even when users are tricked or traditional defenses fail to identify a threat.
Stay ahead in the ever-evolving print industry by browsing our Report Store for the latest insights. Log in to the InfoCenter to view research and studies through our Workplace- and Production-based Advisory Services. Log in to bliQ for product-level research, reports, and specs. Not a subscriber? Contact us for more information.


